Related Topics:
Defense Security Cooperation Agency-
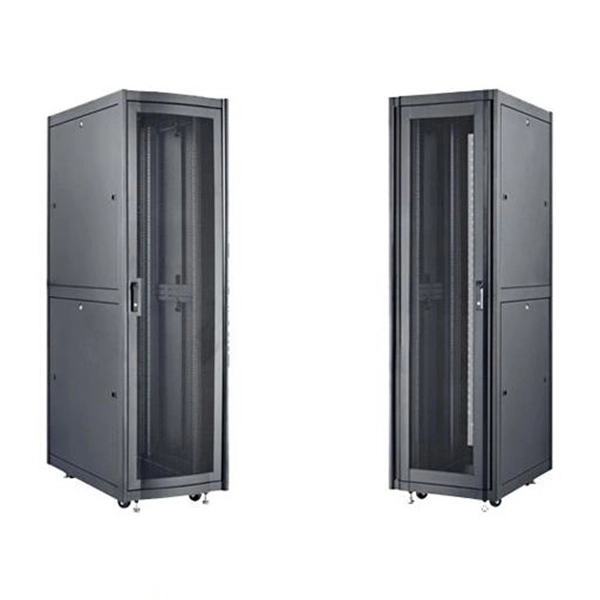
Huijue AI Security Server
The Smart 19-Inch Server Cabinet is the next-generation intelligent rack solution for modern data centers, network rooms, and telecommunication environments. This unit features intelligent temperature monitoring, remote manageability, and intelligent security, giving you full. Can AI-powered monitoring terminals truly bridge the gap between security needs and operational efficiency? As global IoT devices exceed 29 billion in 2023, traditional surveillance systems struggle with false alarms and delayed responses. Huijue Network's products are exported to Europe, North America, Southeast Asia and other countries and. Huijue Networks is a high-tech service manufacturer integrating intelligent network communication equipment and an integrated application of computer intelligent network communication systems. In-depth knowledge of the industry and research and development of innovative technologies, business.
[PDF Version]
-
Network security devices offline
Security cameras can go offline for various reasons, including weak Wi-Fi signals and outdated firmware. Ensuring they have updated. Periodically download the latest Defender security intelligence updates from the Microsoft website. Use a local network share or removable media to distribute these updates to the offline devices. Create Update Scripts: Write PowerShell scripts to automate the installation of updates on offline. I have two FTDs that have been offline for more than a year, and now I can deploy the configuration to change the IP address of the WAN interface to connect to the internet. I now have internet on site, but from a different ISP. We kept working at it and found an interesting solution. d:443 read: connection reset by peer [for support diagnosis: requestID: 7e761b68-a878-915e-af11-2b561484e0e9] "Connection reset by peer"? Not sure where to go.
[PDF Version]
-
Supplier s network security equipment 200G
Powered by a rich set of AI/ML security capabilities that extend into an integrated Fortinet Security Fabric platform, the FortiGate 200G series delivers secure networking that is broad, deep, and automated at any scale. The FortiGate 200G series next-generation firewall (NGFW) combines artificial intelligence (AI)-powered security and machine learning (ML) to deliver threat protection at any scale. Get deeper visibility into your network and see applications, users, and devices before they become threats Powered. Extend the protection capabilities of your Fortinet FortiGate 200G Firewall with comprehensive security services from the AI-powered Fortinet Security Fabric. You can license security services and support à la carte. With a firewall throughput of 3 Gbps and VPN throughput of 6 Gbps, it efficiently handles large volumes of.
[PDF Version]
-
Three-layer protection for network security devices
IT security spans three critical layers: Management, Operational, and Technical controls — not just firewalls and antivirus. Businesses with layered security strategies reduce breach costs by an average of 43% compared to single-layer protection (source: IBM Cost of a Data Breach. To address the threats faced by networks and enhance security protection during network design, construction, and operation, the International Telecommunication Union (ITU) defines a layer- and plane-based security framework in the X. 805 security framework, in. How to design, use, and maintain secure networks. Networks are fundamental to the operation, security and resilience of many organisations. It. This involves deploying multiple levels of security controls to protect against all types of cyberattack, eliminate single points of failure in your network security, and minimize the chance of a data breach.
[PDF Version]
-
Deployment methods for network security devices
This article covers new methods and concepts for security implementation such as the Zero-Trust Architecture, Segmentation and micro-segmentation, Endpoint Detection and Response, and Cloud-based network security, and looks at how AI and machine learning can be applied to security. This plan should begin with identifying your architecture and choosing your deployment method. Deciding how to onboard endpoints to the. Guidance for securing networks continues to evolve as adversaries exploit new vulnerabilities, new security features are implemented, and new methods of securing devices are identified. Improper configurations, role is critical in entire network. All networks are at risk of compromise, especially. As cyber threats continue to grow in sophistication and frequency, organizations must implement robust IDS/IPS deployment strategies that maximize effectiveness while maintaining operational efficiency. Networks are fundamental to the operation, security and resilience of many organisations.
[PDF Version]
-
Which network security equipment brands are available
Several top brands are leading in network security devices in 2025. Channel Insider lists Palo Alto Networks, Fortinet, and Cisco as the top providers. With networks become even bigger and more complex, Cyber Magazine examines the top 10 biggest network security companies so readers can see what's on offer In today's interconnected digital landscape, network security has become paramount for enterprises of all sizes. The company's platform integrates next-generation firewalls, extended detection and response (XDR), and secure access service edge (SASE) capabilities.
-
Qualification Level of Civil Defense Power Distribution Box
Verifiable credentials consist of State, National and/or Local Certifications or Licenses that a Master or Journeyman Electrician may hold, depending on work being performed, and should be identified in the appropriate AHA. The Unified Facilities Criteria (UFC) system is prescribed by MIL-STD 3007 and provides planning, design, construction, sustainment, restoration, and modernization criteria, and applies to the Military Departments, the Defense Agencies, and the DoD Field Activities in accordance with USD (AT&L). This chapter gives general guidance for the preparation of drawings, specifications, and design analyses as related to electrical aspects of military construction projects. The term “Qualified Person (QP)”, as used in this section, refers to “Qualified Person, Electrical”. The information provided here must be utilized by electrical engineers in the development of the plans, specifications, calculations, and Design/Build Request for Proposals (RFP).
[PDF Version]
-
How to seal up civil defense cable trays
When cable trays pass through walls or floors, seal openings using fire-rated penetration sealing materials. Do not modify or damage the tray coating or structure during use. The effective weatherproofing of cable trays helps to keep weather out, preventing damage to the building envelope, avoiding thermal breaks, maintaining the indoor environment and helping to keep the various cables and wires protected. Fire. FIRSTO firestops are designed to seal multi-cable and cable tray penetrations of fire-rated walls and floors. Working in inaccessible openings is often cumbersome. Cables, cable bundles, conduits, bundles of conduits, empty pipes, cable trays and cable ladders may also pass through penetration seals in walls and floors and should be taken into consideration during all phases of design and application. The last part of our penetration seal series of articles. Cable tray installation must comply with specific technical standards to ensure electrical safety, system reliability, and long-term maintainability. 15 is the right general reference, but 501. UL's standard on Type TC says it has a "gas/vaportight continuous sheath," but is silent on whether it can.
[PDF Version]
-
What are the reasons for network security devices
Network security devices are hardware or virtual appliances designed to protect computer networks from unauthorized access, data breaches, and cyberattacks. They include firewalls, intrusion prevention systems, VPN gateways, and other tools that safeguard data across network connections. Whether you manage a large enterprise network or a growing startup infrastructure, these devices. In this article, we will examine eight essential reasons why network security is important and how having strong network security in place benefits your business. This blog explores essential networking devices, including firewalls, IDS/IPS, VPNs, NAC, SIEM, WAFs, and network analyzers, explaining their real-time applications and. Securing network devices is crucial to protect against cyber threats, ensuring data integrity and preventing unauthorized access. Routers, switches, firewalls, and.
[PDF Version]
-
FTTR uses an upgraded version of network security equipment
FTTR is an advanced version of fiber optic technology. It comprises the laying of optical fibers to remote nodes to ensure an entire home or even a building gets access to the robust network. Leisure (Karaoke, Bar, Teahouse. Add security detection mechanism 1. Add conductive contact guards for communication among devices, chip modules and. FTTR can eliminate the need for parallel network infrastructure and multiple intermediate distribution frame (IDF) closets and allows you to reclaim space for more revenue generation with a smaller cable footprint. This paper presents a comprehensive analysis of the FTTR system architecture and protocol stack, focusing on three key technical aspects: centralized. FTTR optimally utilizes fiber optic technology to achieve a robust home optical network. The method is applied to the main gateway equipment and comprises the following steps: acquiring upgrade version information of at least one slave gateway device, and acquiring.
[PDF Version]