Related Topics:
Types Network Security Devices-
Network security devices offline
Security cameras can go offline for various reasons, including weak Wi-Fi signals and outdated firmware. Ensuring they have updated. Periodically download the latest Defender security intelligence updates from the Microsoft website. Use a local network share or removable media to distribute these updates to the offline devices. Create Update Scripts: Write PowerShell scripts to automate the installation of updates on offline. I have two FTDs that have been offline for more than a year, and now I can deploy the configuration to change the IP address of the WAN interface to connect to the internet. I now have internet on site, but from a different ISP. We kept working at it and found an interesting solution. d:443 read: connection reset by peer [for support diagnosis: requestID: 7e761b68-a878-915e-af11-2b561484e0e9] "Connection reset by peer"? Not sure where to go.
[PDF Version]
-
Three-layer protection for network security devices
IT security spans three critical layers: Management, Operational, and Technical controls — not just firewalls and antivirus. Businesses with layered security strategies reduce breach costs by an average of 43% compared to single-layer protection (source: IBM Cost of a Data Breach. To address the threats faced by networks and enhance security protection during network design, construction, and operation, the International Telecommunication Union (ITU) defines a layer- and plane-based security framework in the X. 805 security framework, in. How to design, use, and maintain secure networks. Networks are fundamental to the operation, security and resilience of many organisations. It. This involves deploying multiple levels of security controls to protect against all types of cyberattack, eliminate single points of failure in your network security, and minimize the chance of a data breach.
[PDF Version]
-
What are some digital network security devices
The main types of network security devices include firewalls, intrusion protection systems (IPS), unified threat management (UTM) systems, network access control (NAC), email security gateways, web application firewalls (WAF), and VPN gateways. These devices act as barriers between the internal network and potential threats from the outside world. Whether you're a business owner or an IT professional, understanding the. Explore essential security devices in networking with this beginner's guide, covering firewalls, VPNs, IDS, IPS, and more. Firewall appliances and intrusion detection systems are critical components of network security. Top network. Network security solutions are specialized hardware devices designed to protect networks from cyber threats, and modern innovations like Juniper Mist networking for secure, scalable infrastructure further enhance visibility, automation, and overall network performance.
[PDF Version]
-
Deployment methods for network security devices
This article covers new methods and concepts for security implementation such as the Zero-Trust Architecture, Segmentation and micro-segmentation, Endpoint Detection and Response, and Cloud-based network security, and looks at how AI and machine learning can be applied to security. This plan should begin with identifying your architecture and choosing your deployment method. Deciding how to onboard endpoints to the. Guidance for securing networks continues to evolve as adversaries exploit new vulnerabilities, new security features are implemented, and new methods of securing devices are identified. Improper configurations, role is critical in entire network. All networks are at risk of compromise, especially. As cyber threats continue to grow in sophistication and frequency, organizations must implement robust IDS/IPS deployment strategies that maximize effectiveness while maintaining operational efficiency. Networks are fundamental to the operation, security and resilience of many organisations.
[PDF Version]
-
What are the reasons for network security devices
Network security devices are hardware or virtual appliances designed to protect computer networks from unauthorized access, data breaches, and cyberattacks. They include firewalls, intrusion prevention systems, VPN gateways, and other tools that safeguard data across network connections. Whether you manage a large enterprise network or a growing startup infrastructure, these devices. In this article, we will examine eight essential reasons why network security is important and how having strong network security in place benefits your business. This blog explores essential networking devices, including firewalls, IDS/IPS, VPNs, NAC, SIEM, WAFs, and network analyzers, explaining their real-time applications and. Securing network devices is crucial to protect against cyber threats, ensuring data integrity and preventing unauthorized access. Routers, switches, firewalls, and.
[PDF Version]
-
Network optical module interface types
Common optical module types such as SFP, GBIC, XFP, and XENPAK, along with optical interfaces like FC, SC, and LC, each have their unique characteristics that make them suitable for specific application scenarios. Optical modules typically have an electrical interface on the side that connects to the inside of the system and an optical interface on the side that connects to the outside. An optical module usually consists of an optical transmitting device (TOSA, including a laser), an optical receiving device (ROSA, including a photodetector), functional circuits,main control circuit board (PCBA), housing and optical (electrical) interface and other components. Think of it as the “translator” for your network equipment, converting electrical signals into optical signals. This guide provides a clear, practical comparison among the most common transceiver types - GBIC, SFP, XFP, and SFP+ - to help you make informed procurement decisions. com, we specialize in Cisco-compatible and NS Comm transceivers, offering enterprise customers tested, certified. Optical modules are available in various types to meet diversified requirements.
[PDF Version]
-
What types of network cabinets include power distribution cabinets
The most common types include distribution cabinets, control panel enclosures, network cabinets, switchgear cabinets, and junction boxes. It ensures that electricity is delivered safely and efficiently to different sections of a building or facility. In electrical engineering, a power distribution cabinet refers. The Liebert® RXV remote power distribution cabinet provides dense power distribution in a small footprint, with up to 400 Amp inputs and 84 poles in a single 24”x12” panelboard. Learn More Designed to provide 50-300 kVA power in small to mid-sized data centers, the Liebert® TFX PDU offers reliable. Electrical cabinets are specialized enclosures designed to house electrical components, controls, and distribution systems in industrial and commercial settings. Despite their critical importance, these cabinets often remain an overlooked element of infrastructure in both industrial and. A network cabinet PDU plays a critical role in IT infrastructure by distributing power to devices housed in server racks. Without proper power management, systems risk downtime, as 43% of IT outages stem from power-related issues.
[PDF Version]
-
A Simple Explanation of SD-WAN Network Devices
SD-WAN is a software-defined networking overlay for WAN infrastructure that gives organizations more control over how their networks operate and grow. Many choose it when older WAN models slow expansion or create more work for IT. Typically, dedicated Multiprotocol Label Switching (MPLS) circuits were used to help ensure security and reliable connectivity. This doesn't work in a. A software-defined wide area network (SD-WAN) connects local area networks (LANs) across large distances using controlling software that works with a variety of networking hardware. Learning Center / the network layer / What is enterprise networking? How to migrate from MPLS How to prepare for. A Software-Defined Wide Area Network (SD-WAN) is a networking technology that leverages software-defined networking (SDN) principles to enhance WAN performance. They are currently the go-to tech for connecting branch offices, HQ.
[PDF Version]
FAQs about A Simple Explanation of SD-WAN Network Devices
What are the benefits of SD WAN?
1. Deliver superior quality of experience at any scale2. Accelerate network and security convergence, and simplify WAN architecture3. Orchestrate c...
What is SD WAN?
SD-WAN is a software-defined approach to managing the WAN. SD-WAN is used for better security.
What is the difference between WAN and SD WAN?
SD-WAN allows remote sites to connect more easily to networks, data centers, and/or multiple-clouds with lower latency, better performance, and mor...
-
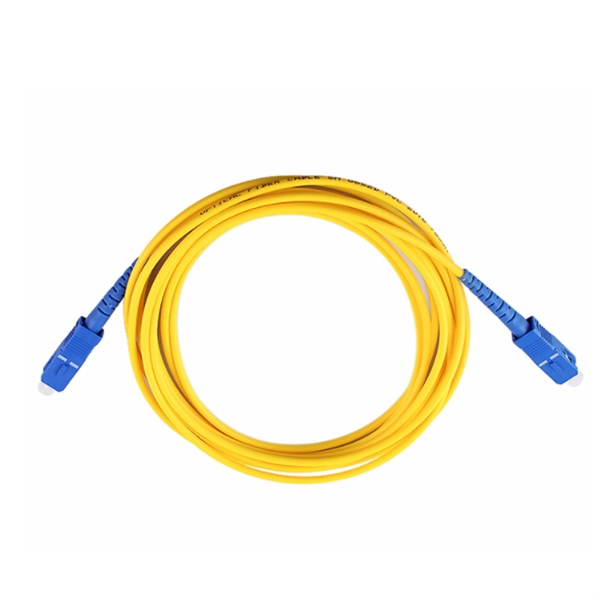
Ncm-f Multimode Fiber Optic Network Interface Card
The Notifier NCM-F Network Communications Module (NCM) provides NOTIFIER's NFS-640, NFS-3030, and NFS2-3030 Fire Alarm Control Panels, and NCA and NCA-2 Network Control Annunciators with a means to connect to NOTI•FIRE•NET. NCM-F connects nodes with Fiber-Optic cable.
-
Recommended information on explosion-proof network cabinets
Explosion-proof switch cabinets must follow strict rules like IEC, NEC, and NFPA. These rules help keep people safe in dangerous places. These specifications dictate the design, manufacturing, and installation of electrical safety systems, directly impacting project outcomes. Explosion-proof cabinets are specialized storage units engineered to safely contain flammable or reactive materials that could ignite under certain conditions. The notices referring to your personal safety are highlighted in the manual by a safety alert symbol, notices referring only to property damage have no safety alert. The new EXpressure cabinets are revolutionising the science of explosion protection.
-
How many network cables can a telecom server chassis connect to
When cabling an individual chassis, connect one network cable from each management module to the data center top of rack switch. Ensure that both ports on the top of rack switch are enabled and on the same network and VLAN. The MX7000 chassis features dual redundant management modules, with each management module featuring two management network ports, for a total of 4 management network ports on the chassis. The management network is meant to provide network connections for chassis management separate from the. To help with cable management, allow additional space in the rack above and below the chassis to make it easier to route copper cables (plus up to eight copper cables per Cisco UCS 5108 server chassis) through the rack. Network racks are typically 19” wide and not as deep as server racks. Outages, downed systems, data transmission errors — even overheating or fires can occur with power cables. This section covers topics listed in the following table.
[PDF Version]